Trust Centre
Trust is earned, not declared
As a unified governance platform, we hold ourselves to the same standards across every domain we help you govern. Transparency is our foundation.
- Multi-tenant isolation
- TLS 1.3 + AES-256 encryption
- EU data residency
- SSO & MFA enforced
- Data Protection by Design
- Security by Design
- Responsible AI Built-In
- Risk-Managed Operations
Our Trust Pillars
Foundational commitments that guide how we build, operate, and evolve our platform.
Privacy
Our commitment to data protection and privacy by design
Click to learn more
Security
Enterprise-grade security embedded throughout our platform
Click to learn more
Availability
Clear information about service health and availability
Click to learn more
Compliance
Aligned with international standards and frameworks
Click to learn more
Responsible AI
Human-centric AI with transparency and oversight
Click to learn more
Ethics
Integrity, accountability, and ethical business practices
Click to learn more
Certifications & Compliance
We're committed to achieving and maintaining industry-recognized certifications. Here's our current status and roadmap.
ISO/IEC 27001
Information Security Management System
Target: 2026
SOC 2 Type II
Security, Availability & Confidentiality Controls
Target: 2027
ISO 27701
Privacy Information Management System
Target: 2027
GDPR Compliance
EU General Data Protection Regulation
Our Commitment to Transparency
We believe in being honest about where we are on our certification journey. As a governance platform, we understand the importance of these standards and are actively working toward achieving them. We'll update this page as we progress.
Platform Security
Security is embedded throughout our platform, from architecture to operations. We use the same governance tools we build to manage our own security posture.
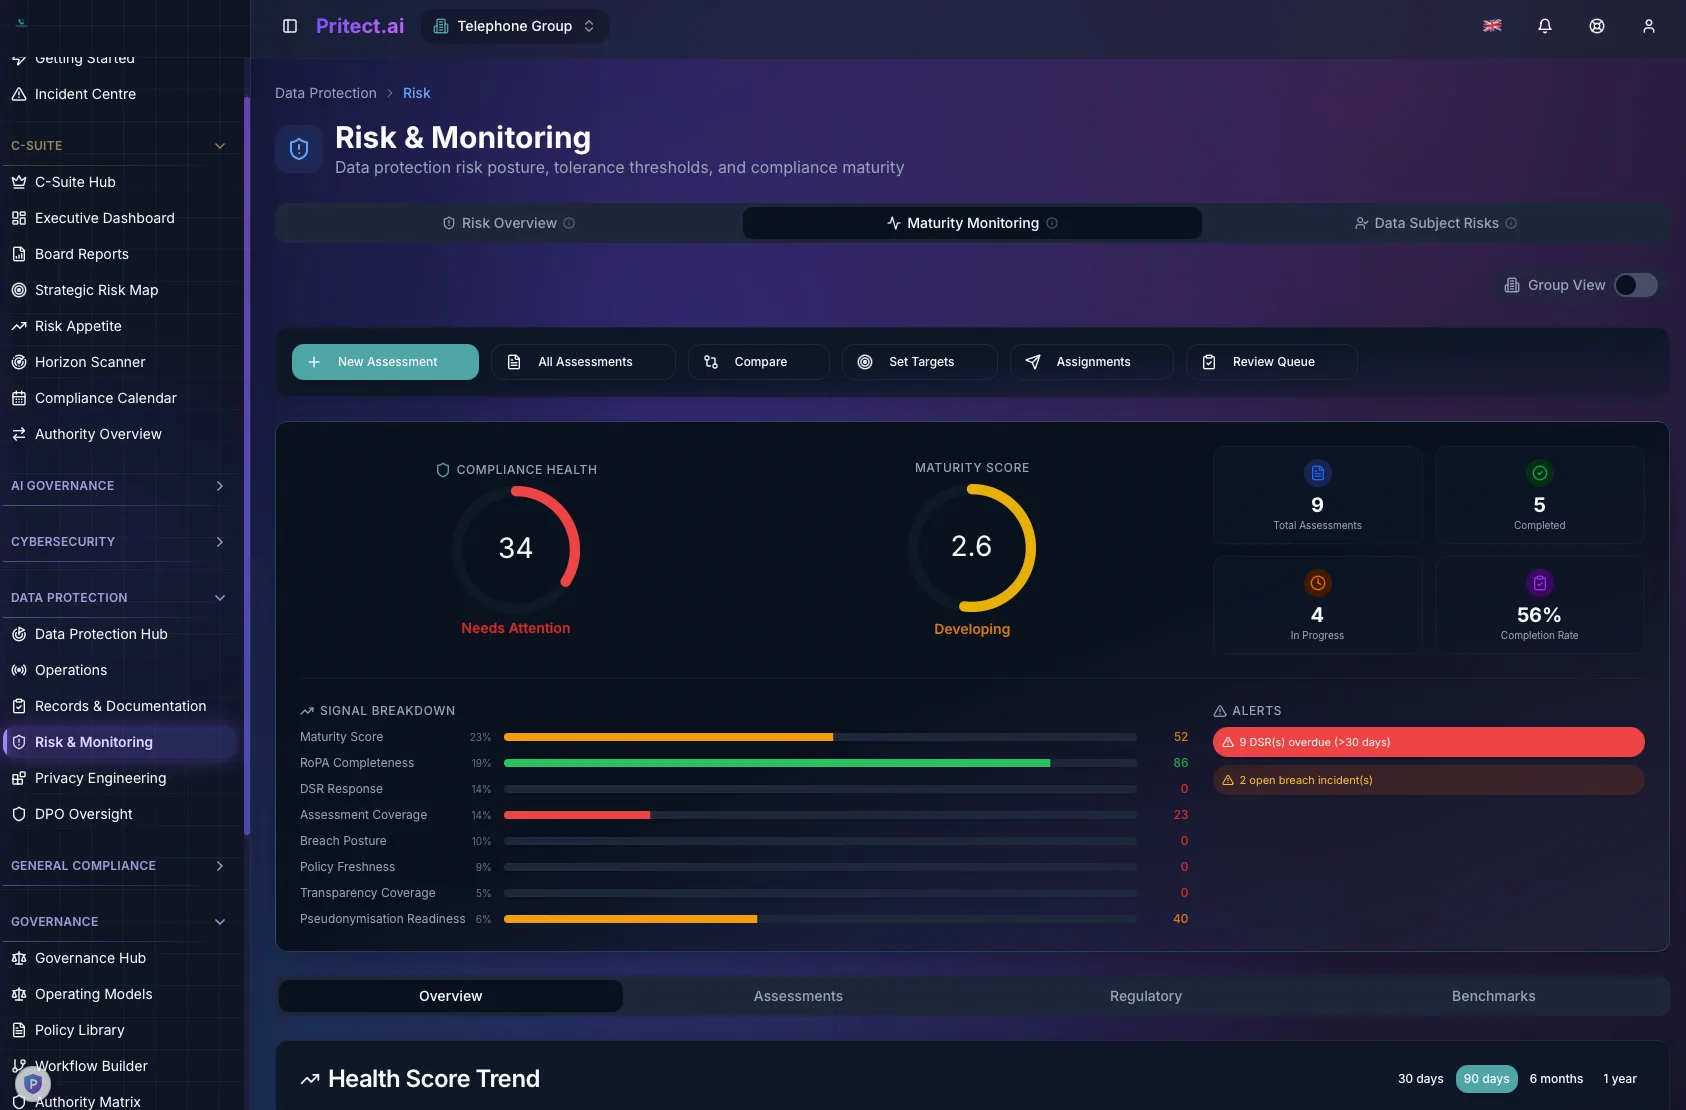
Pritect's maturity assessment framework, the same tools we use internally to track our security posture
Multi-Tenant Architecture
Complete tenant isolation enforced by the database itself: row-level security on every tenant table, with cross-tenant access denied by design.
Encryption Standards
TLS 1.3 for data in transit, AES-256 for data at rest. All sensitive fields encrypted at the application level.
Role-Based Access Control
Granular RBAC with platform, tenant, module, and entity-level permissions. Custom roles supported.
Authentication & SSO
Enterprise SSO via Azure AD, Google Workspace, and SAML/OIDC. MFA with step-up enforcement, available on every account by policy.
Comprehensive Audit Logging
Every action logged with user, timestamp, and context. Audit logs retained for compliance periods.
Secure Infrastructure
Hosted on enterprise-grade cloud infrastructure with DDoS protection, WAF, and automatic scaling.
Continuous Monitoring
Continuous automated monitoring with threat detection, alerting, and regular vulnerability scanning.
Incident Response
Documented incident response procedures with defined SLAs, run on the same Incident Centre we ship to customers.
Service status and availability
For the latest information we have about Pritect's availability, use our public status page. It shows the results of configured monitors and any service updates we have published.
Public status page
Check the current reported status
Conditions can change quickly, so we do not reproduce a status snapshot here. Open the status page for the most recent monitor results and published notices.
Current monitor results
The latest reported state for the services monitored on the status page.
Recent history
Recorded uptime history for each listed monitor, where data is available.
Incident updates
Updates we publish while investigating and resolving a service incident.
Planned maintenance
Notices for scheduled work that may affect service availability.
The status page reflects the monitors and notices currently configured. It may not identify every customer-specific issue or show a newly developing incident immediately. If your experience differs from the reported status, please contact support.
Responsible AI
AI Governance You Can Verify
Pritect embeds the same governance rigour in its own AI that it helps organisations implement. Every AI feature is designed around transparency, human oversight, and data sovereignty, backed by documented controls, not just promises.
Powered by Mistral, European AI
Pritect's AI features are powered by Mistral, a leading European AI company headquartered in Paris. Mistral is included in the platform and serves every organisation by default, so AI processing aligns with EU data sovereignty principles, GDPR expectations, and the values of organisations operating in regulated environments. All AI interactions are stateless: your data is never retained, stored, or used for model training.
Organisations on an enterprise plan that prefer a different AI provider may select one, currently Mistral, OpenAI, Anthropic or Google, using their own API key and their own agreement with that provider. The choice applies to the chat-based AI features and to the whole organisation. Document OCR, voice transcription and knowledge-base embeddings always remain on Pritect's EU-hosted Mistral, and there is no silent fallback: if a customer's own provider fails, the call fails rather than rerouting their data. Retention and training terms for a provider a customer brings are governed by that customer's own agreement with it.
- European Headquarters
- Stateless Processing
- Zero Data Retention
Core Principles
Human Oversight Required
All AI outputs are advisory only. Every recommendation requires explicit human review and approval before any action is taken. AI augments professional judgment. It never replaces it.
No Training on Your Data
Customer data is never used to train, fine-tune, or improve AI models. All interactions are stateless API calls: your data is processed, the response returned, and nothing retained.
European AI Infrastructure
Powered by Mistral, a European-headquartered AI provider, included in the platform and serving every organisation by default. AI processing aligns with European data sovereignty principles and EU regulatory expectations. Enterprise customers who prefer a different provider may select one.
No Self-Learning
Pritect's AI does not learn, adapt, or evolve based on usage. No feedback loops, no reinforcement learning, no model drift. Every request is processed independently.
Tenant Isolation & Data Minimisation
Strict tenant-level isolation ensures no cross-contamination between organisations. AI features operate on the minimum data necessary to produce the requested output.
Input Sanitisation & Prompt Protection
All inputs to AI features are sanitised and validated. Prompt injection protections prevent manipulation of AI behaviour through crafted inputs.
AI Clearly Labelled
Every AI-generated output is explicitly labelled as AI-assisted. Users always know when they are viewing AI-generated content versus human-authored information.
EU AI Act Aligned
Pritect's AI features are classified as non-high-risk under the EU AI Act. No biometric identification, emotion recognition, social scoring, or autonomous decision-making.
Detailed AI Governance
Data Processing & Sovereignty
Security & Isolation
Human Oversight & Control
Regulatory Classification & Compliance
Monitoring & Transparency
AI-Powered Capabilities
Pritect integrates AI across governance workflows to accelerate analysis, surface risks, and reduce manual effort, always under human supervision.
- Risk assessment and scoring
- Compliance gap identification
- Regulatory horizon scanning
- Legal obligation triage
- PII detection and classification
- Evidence matching and correlation
- Policy document summarisation
- Board report generation
- Security control recommendations
- Assessment recommendations
- Supplier risk analysis
- Control effectiveness evaluation
Documentation
Access our compliance documentation. Some documents require verification for access.
Publicly Available
Master Service Agreement
Terms and conditions for using Pritect.ai
Implementation Services Terms
Terms governing onboarding, configuration, and platform consulting
Data Processing Agreement
Standard DPA for customers processing personal data
Sub-processor List
List of third parties who process data on our behalf
Acceptable Use Policy
Permitted and prohibited uses of the platform
Third-Party Licences
Open source software licences and attributions
Privacy Notice
How we collect, use, and protect your personal data
Cookie Notice
Cookies used on this website and their purposes
Security Architecture
Overview of Pritect.ai's security architecture and controls
Penetration Test Report
Independent white box penetration test of the Pritect.ai platform, May 2026
Request Access
ISO/IEC 27001:2022
Information security management system certification
Coming 2026Consensus Assessment Initiative Questionnaire (CAIQ)
Cloud security self-assessment responses
Available on requestFrequently asked questions
Security Inquiries
Get in Touch
Have security questions or need documentation access? We respond to all inquiries within 2 business days.