Enterprise Risk
Management
Unified risk management across all governance domains, from atomic feeder risks to enterprise principal risk, with a 4-level hierarchy, AI-powered analysis, and cross-domain aggregation built for ISO 31000.
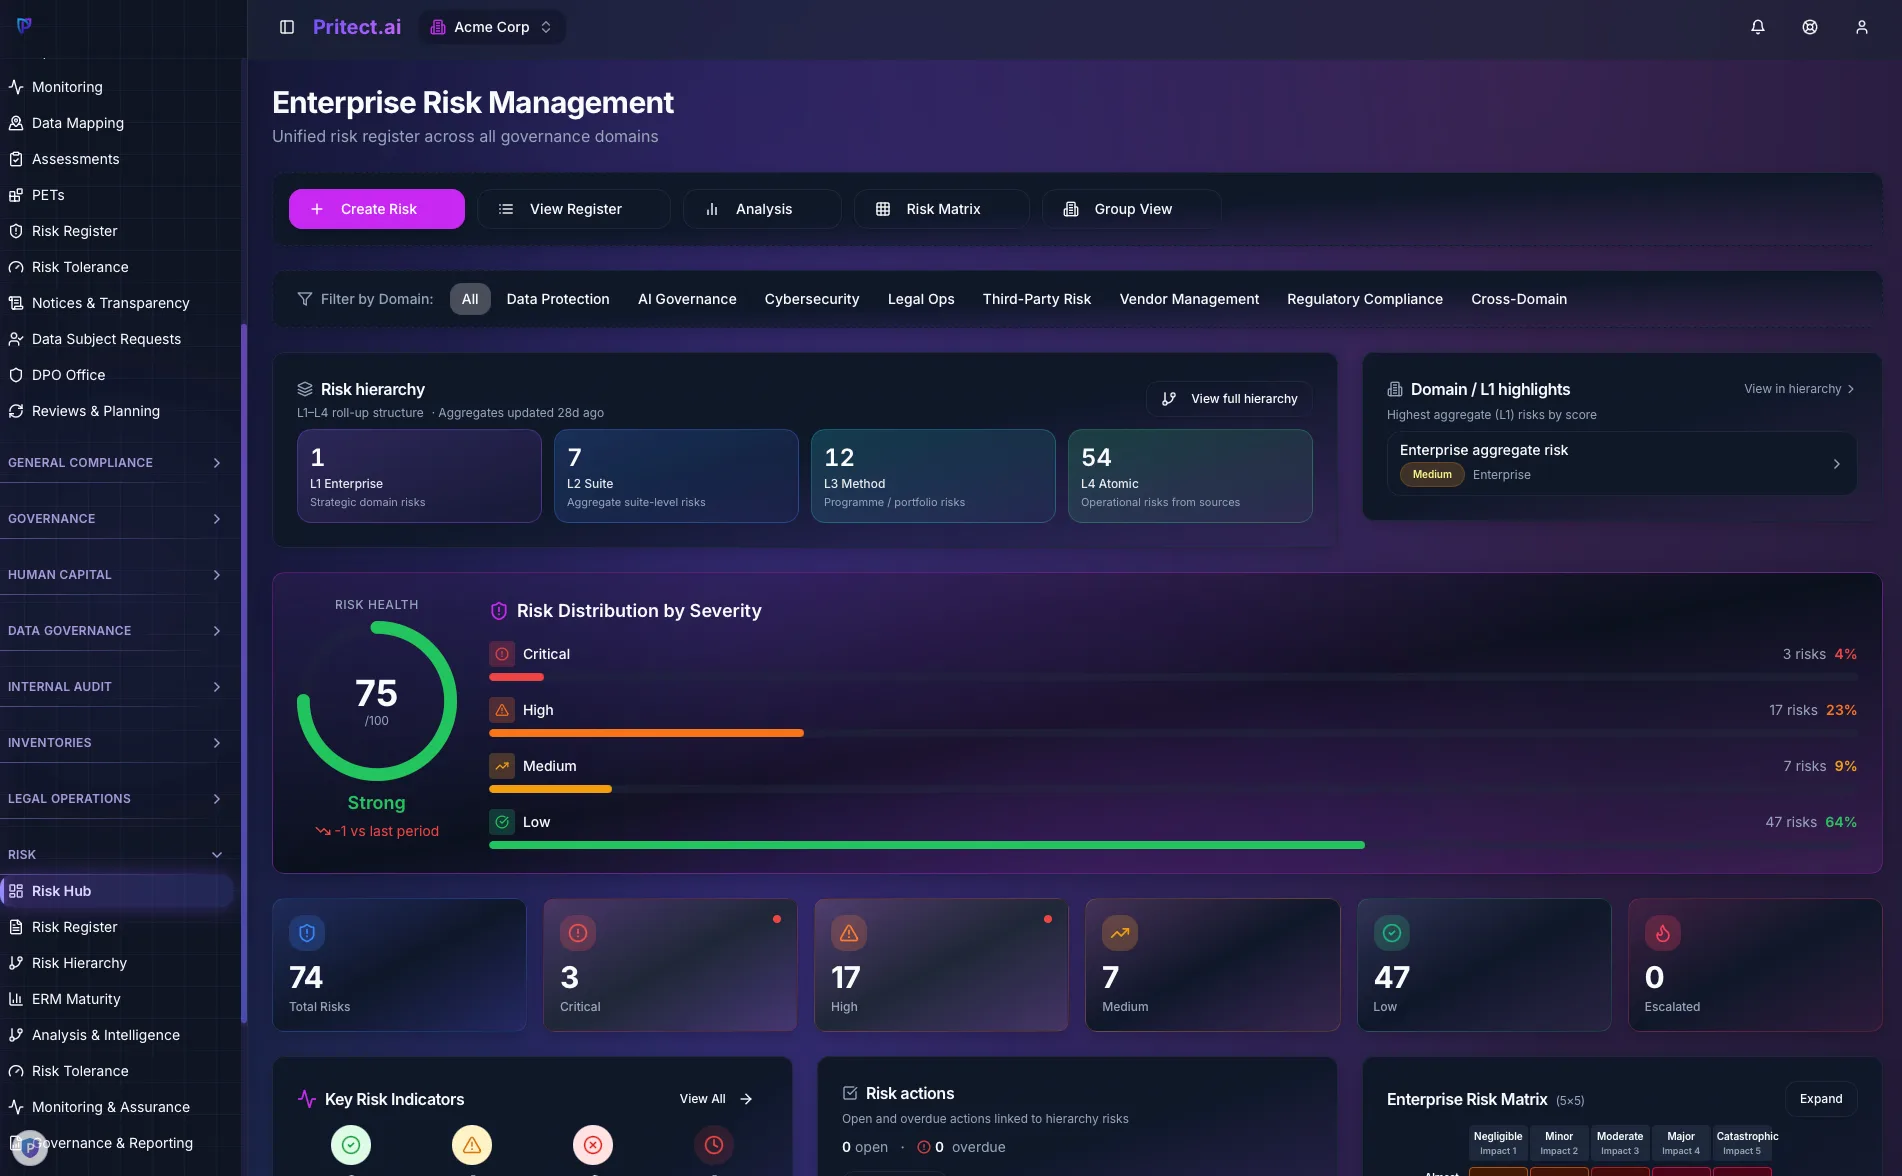
Unified across every governance domain
One risk register. Every domain. Filter by Data Protection, AI, Cybersecurity, Legal, Supplier, and more.
- Data Protection
- AI Governance
- Cybersecurity
- Legal Ops
- Third-Party Risk
- Supplier Management
- Regulatory Compliance
- Cross-Domain
The Risk Management Lifecycle
From identifying risks to aggregating them into a single enterprise view, a structured approach aligned with ISO 31000.
Identify
Discover risks across every domain
Capture and categorise risks across every governance domain, from data protection and AI governance to cybersecurity, legal, supplier and regulatory compliance, on a unified four-level hierarchy running from enterprise principal risks down to atomic feeder risks.
- Unified Risk Register across every governance domain
- Filter by domain, owner, entity or treatment status
- L1 to L4 Risk Hierarchy with Roll-Up
- Risk Ownership & Accountability
- Sync Suite Risks, Auto-Import from All Modules
Assess
Score with configurable matrices
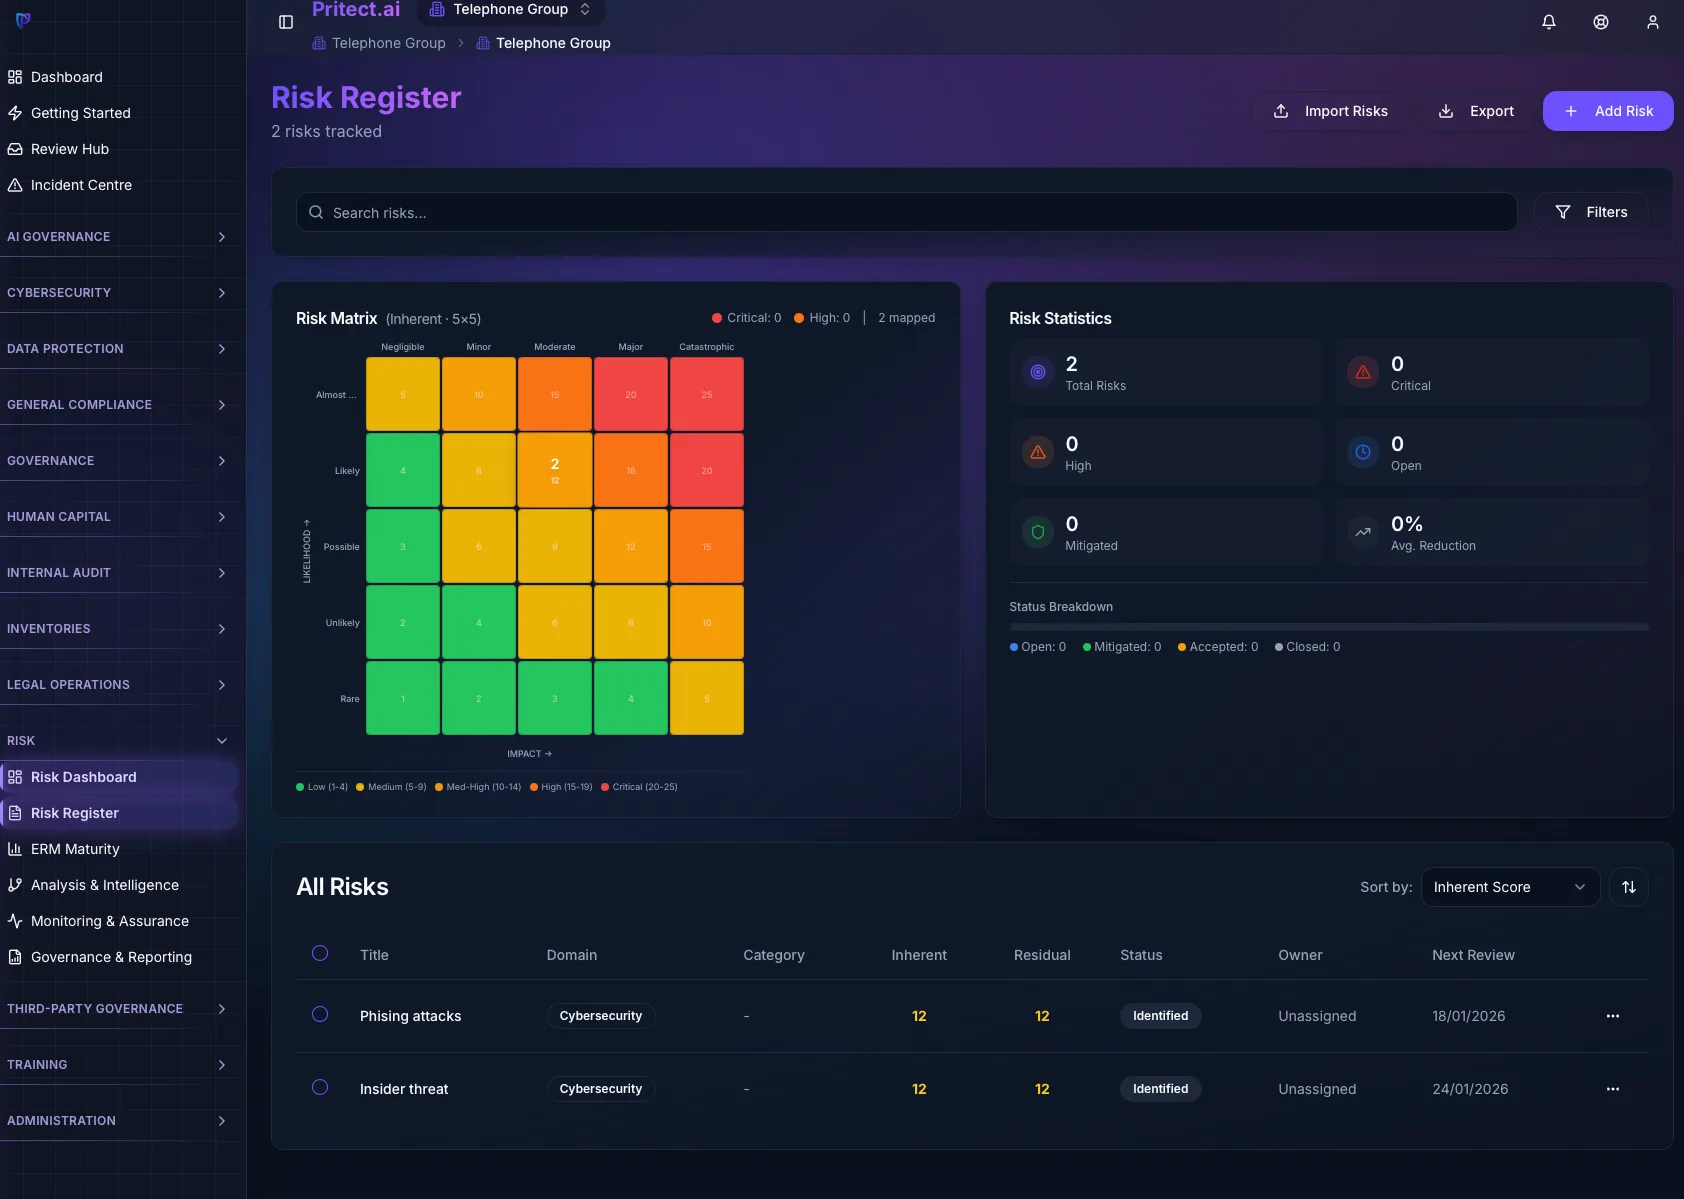
Score risks using configurable 3x3, 4x4 or 5x5 matrices with inherent and residual scoring, colour-coded heat maps, and automatic severity classification. The interactive risk matrix visualises your entire risk landscape at a glance.
- 5×5 Interactive Risk Matrix (colour-coded)
- Inherent & Residual Score Tracking
- Risk Distribution by Severity
- ISO 31000 & COSO ERM Alignment
- Status Breakdown (Open, Mitigated, Accepted, Closed)
Analyse
Advanced risk intelligence
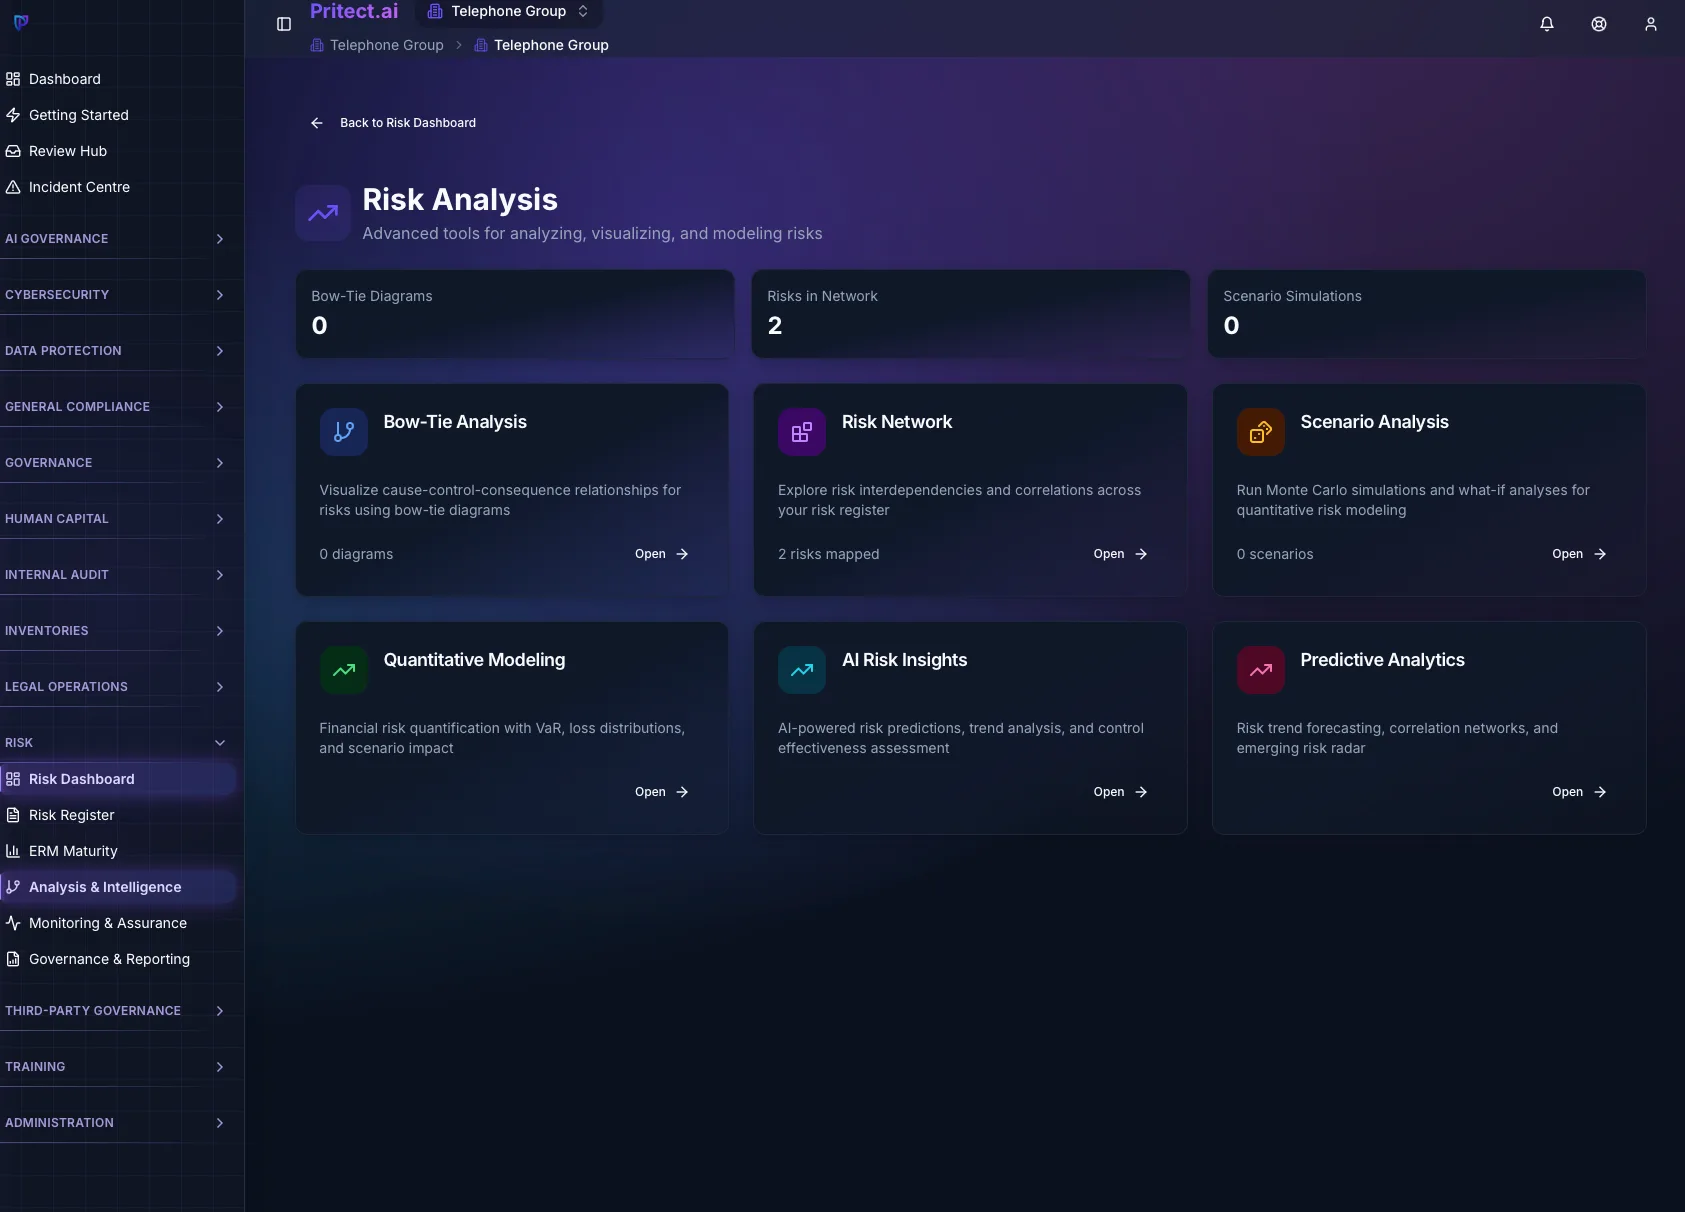
Go beyond static registers with bow-tie analysis, risk network mapping, Monte Carlo scenario simulations, and AI-powered auto insights that surface feeder sync gaps and unlinked KRIs, so you know exactly where to focus.
- Bow-Tie Analysis (cause → control → consequence)
- Risk Network showing interdependencies and cascade paths
- Scenario Simulation (Monte Carlo)
- Auto Insights, AI-Detected Gaps & Actions
- Quantitative Modelling & Financial Valuation
Aggregate
Enterprise-wide roll-up
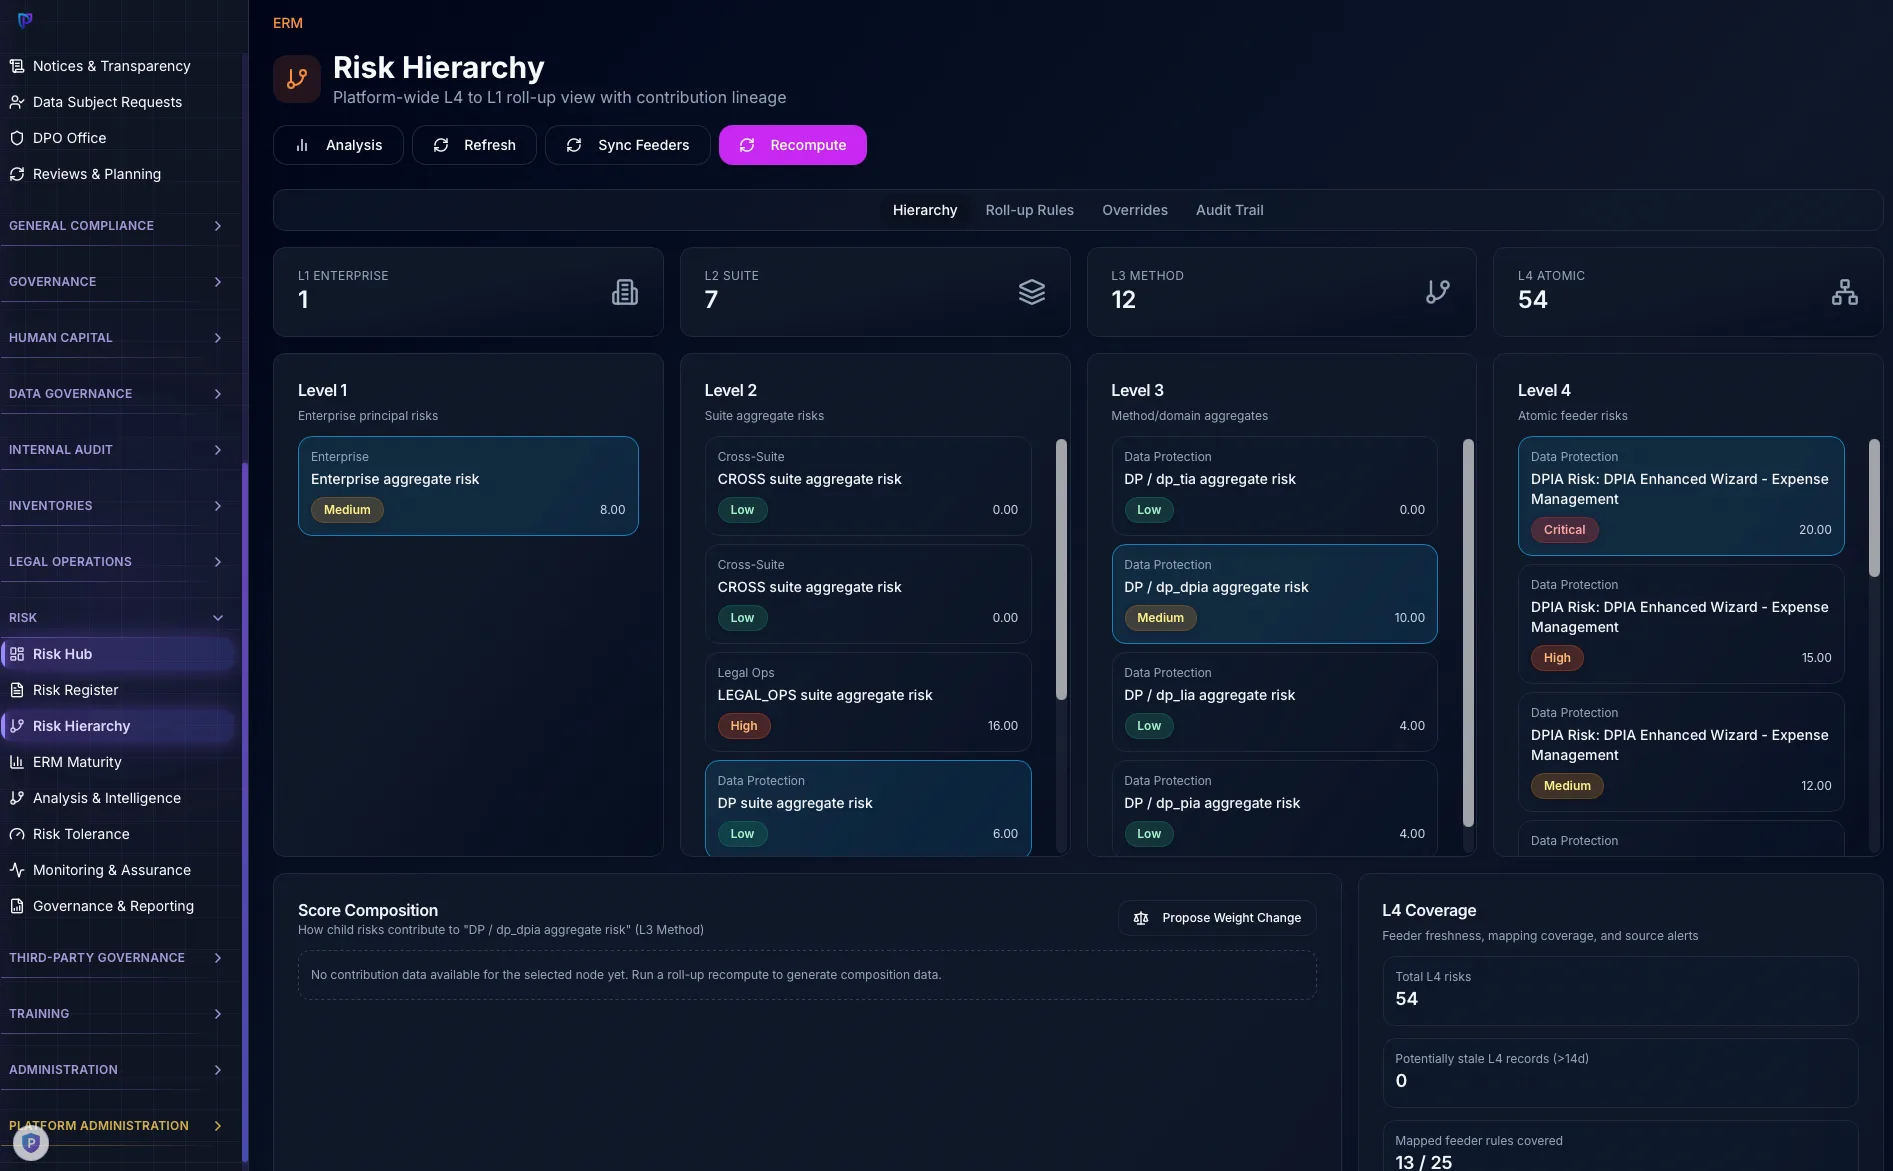
A platform-wide L1 to L4 risk hierarchy with automatic contribution lineage: atomic feeder risks (L4) roll up into method aggregates (L3), suite aggregates (L2), and a single enterprise principal risk (L1). Recompute scores, propose weight changes, and track feeder coverage.
- L1 Enterprise → L2 Suite → L3 Method → L4 Atomic
- One-Click Recompute with Score Composition
- Roll-Up Rules & Override Management
- Feeder coverage, so you can see what is not rolling up
- Full Audit Trail per Hierarchy Node
Key Risk Indicators
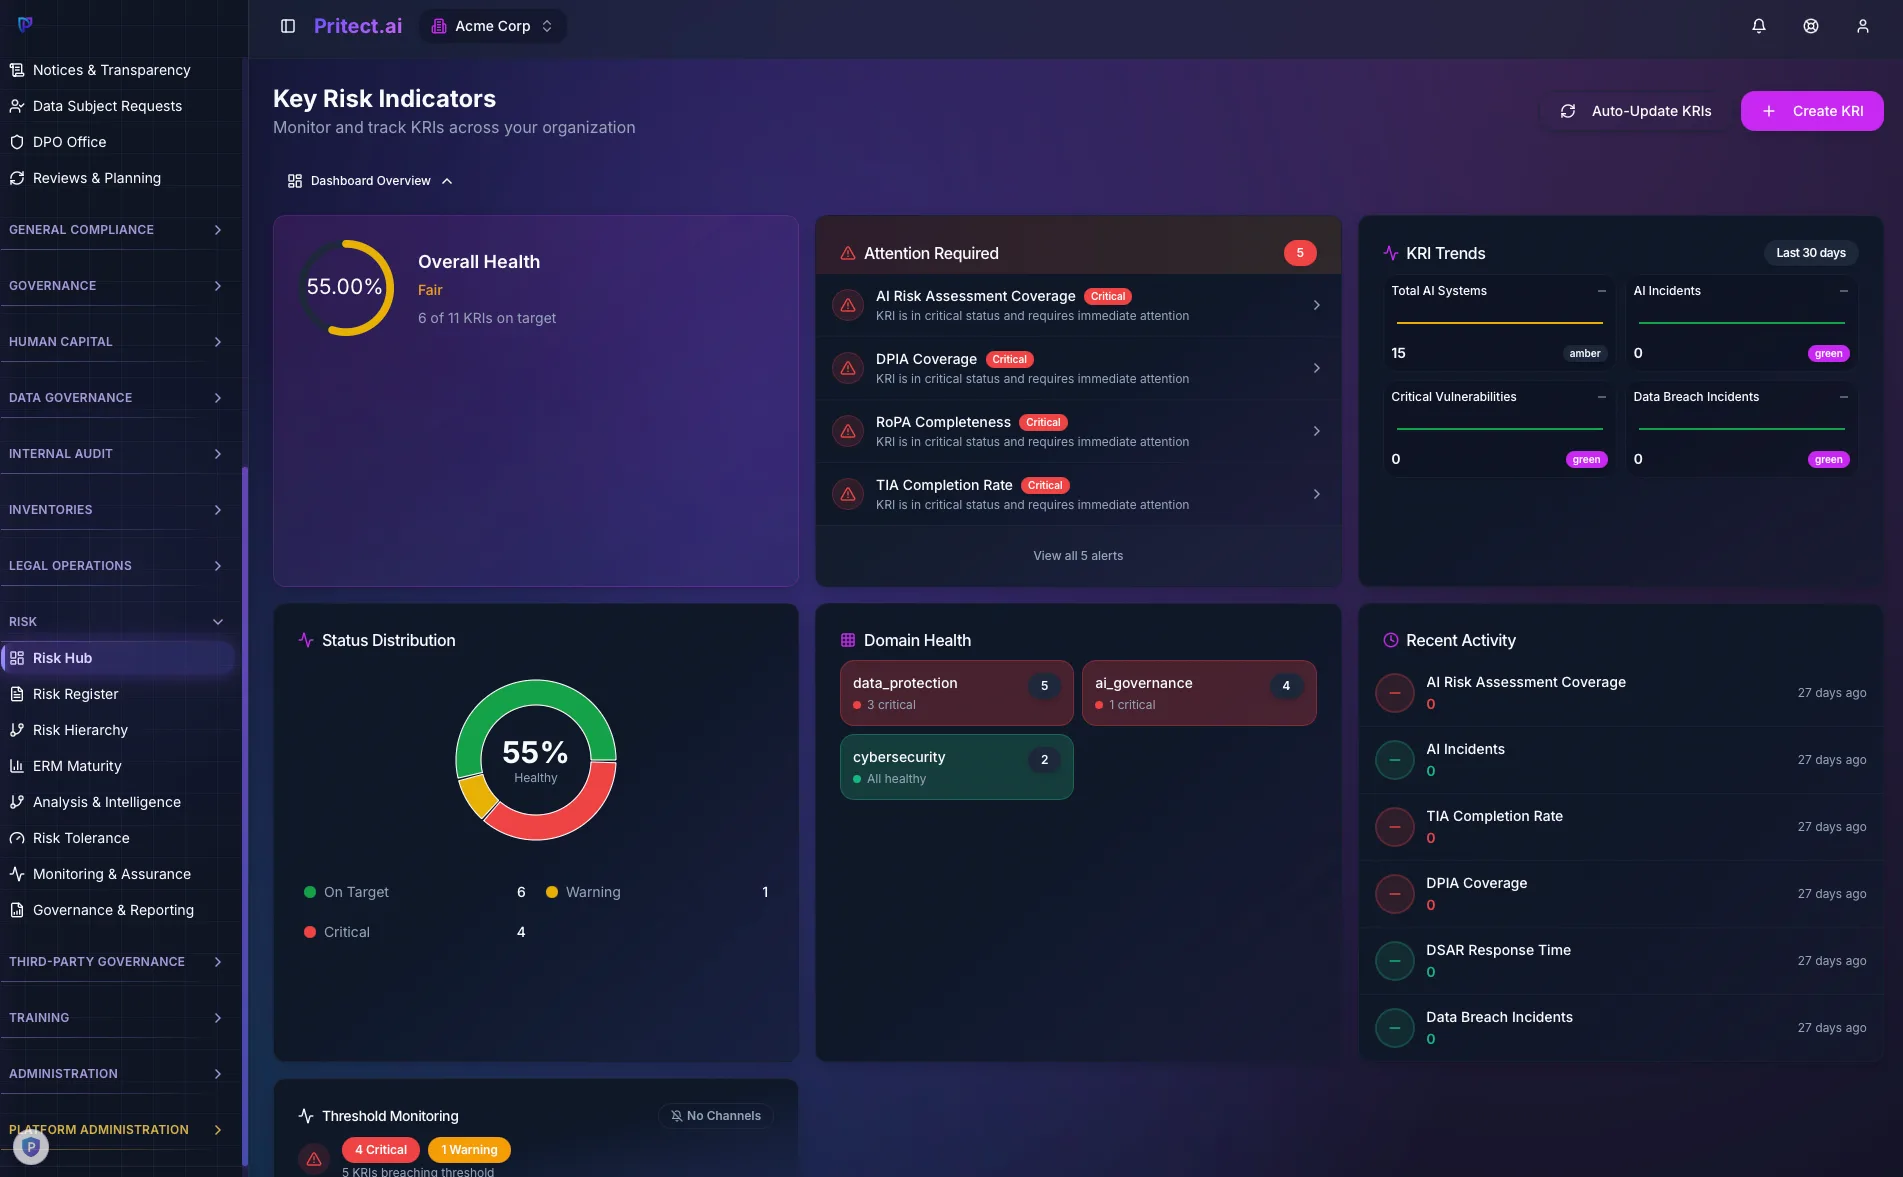
Track indicators against traffic-light thresholds with automatic escalation. The dashboard surfaces an overall health score, the indicators needing attention, trend sparklines and status distribution across every domain.
- Overall KRI Health Score with trend tracking
- Attention Required panel, critical KRIs surfaced
- KRI Trends (30d sparklines per indicator)
- Domain Health, per-domain KRI breakdown
- Threshold Monitoring with channel alerts
- Auto-Update KRIs from platform data
Risk Intelligence at Your Fingertips
Six ways to interrogate the same register, so the answer you take to the board is the one the register actually supports.
Bow-tie analysis
Causes, barriers and consequences on one diagram
Scenario simulation
Monte Carlo across correlated risks
Quantitative modelling
Value at risk and loss distribution
Risk network
Interdependencies and cascade paths
Predictive analytics
Where the register is trending
Register quality
Gaps and stale entries, surfaced not hidden
Enterprise-Ready Capabilities
Built for complex organisations with multi-entity structures, regulatory requirements, and mature governance frameworks.
Multi-Entity Support
Manage risks across complex corporate structures with cascading policies, group views, and entity-specific risk profiles and scoring.
ISO 31000 & COSO ERM
Built-in alignment with ISO 31000 risk management principles and COSO ERM framework terminology and methodology.
Three Lines of Defence
Integrate risk management, compliance, and internal audit functions in a unified three lines model with assurance mapping.
ERM Maturity Assessment
Assess and track your risk management maturity across governance, process, and culture dimensions with entity-level comparison.
Risk Committee Hub
Manage risk committees with agenda planning, meeting records, escalation tracking, and action follow-up.
Board Report Wizard
Generate board-ready risk reports with automated data aggregation, executive summaries, and trend analysis.
Control Testing
Schedule, execute, and track control effectiveness testing with test plans, evidence collection, and result analysis.
Monitoring & Assurance
Centralised assurance activities with integrated coverage mapping, threshold monitoring, and automated alert channels.
Risk Appetite and Tolerance
Appetite statements with tolerance bands per domain, and breaches recorded when a risk moves outside them, so appetite is a live control rather than a paragraph in last year’s policy.
Emerging Risks
Track what is forming before it reaches the register, through monitoring, escalation and the point at which a risk materialises.
Ready to unify your enterprise risk management?
From atomic feeder risks to enterprise principal risk, one platform, one hierarchy, one source of truth.
From the resource library
Related guides and analysis
- Perspective
The governance organisation of tomorrow
Accountability is an operational discipline, not a documentation exercise. How the privacy operating model extends across privacy, cyber, and AI, and the system that makes it real.
8 min read - Explainer
Unified GRC vs point tools
Why stitching together separate tools for data protection, AI, cybersecurity, and risk creates reconciliation work, what a shared data model changes, and the honest trade-off.
6 min read