The Foundation Every Governance Domain Builds On
Your assets, suppliers, and customers are the shared data layer that connects every live governance domain, from Data Protection, Cybersecurity and AI Governance to Enterprise Risk and Incident Management.
One source of truth. Multiple compliance perspectives. Zero duplication.
Inventories
Assets • Suppliers • Customers
Health Scoring
Track inventory completeness
Domain Breakdown
See coverage at a glance
Cross-Domain Stats
Unified visibility
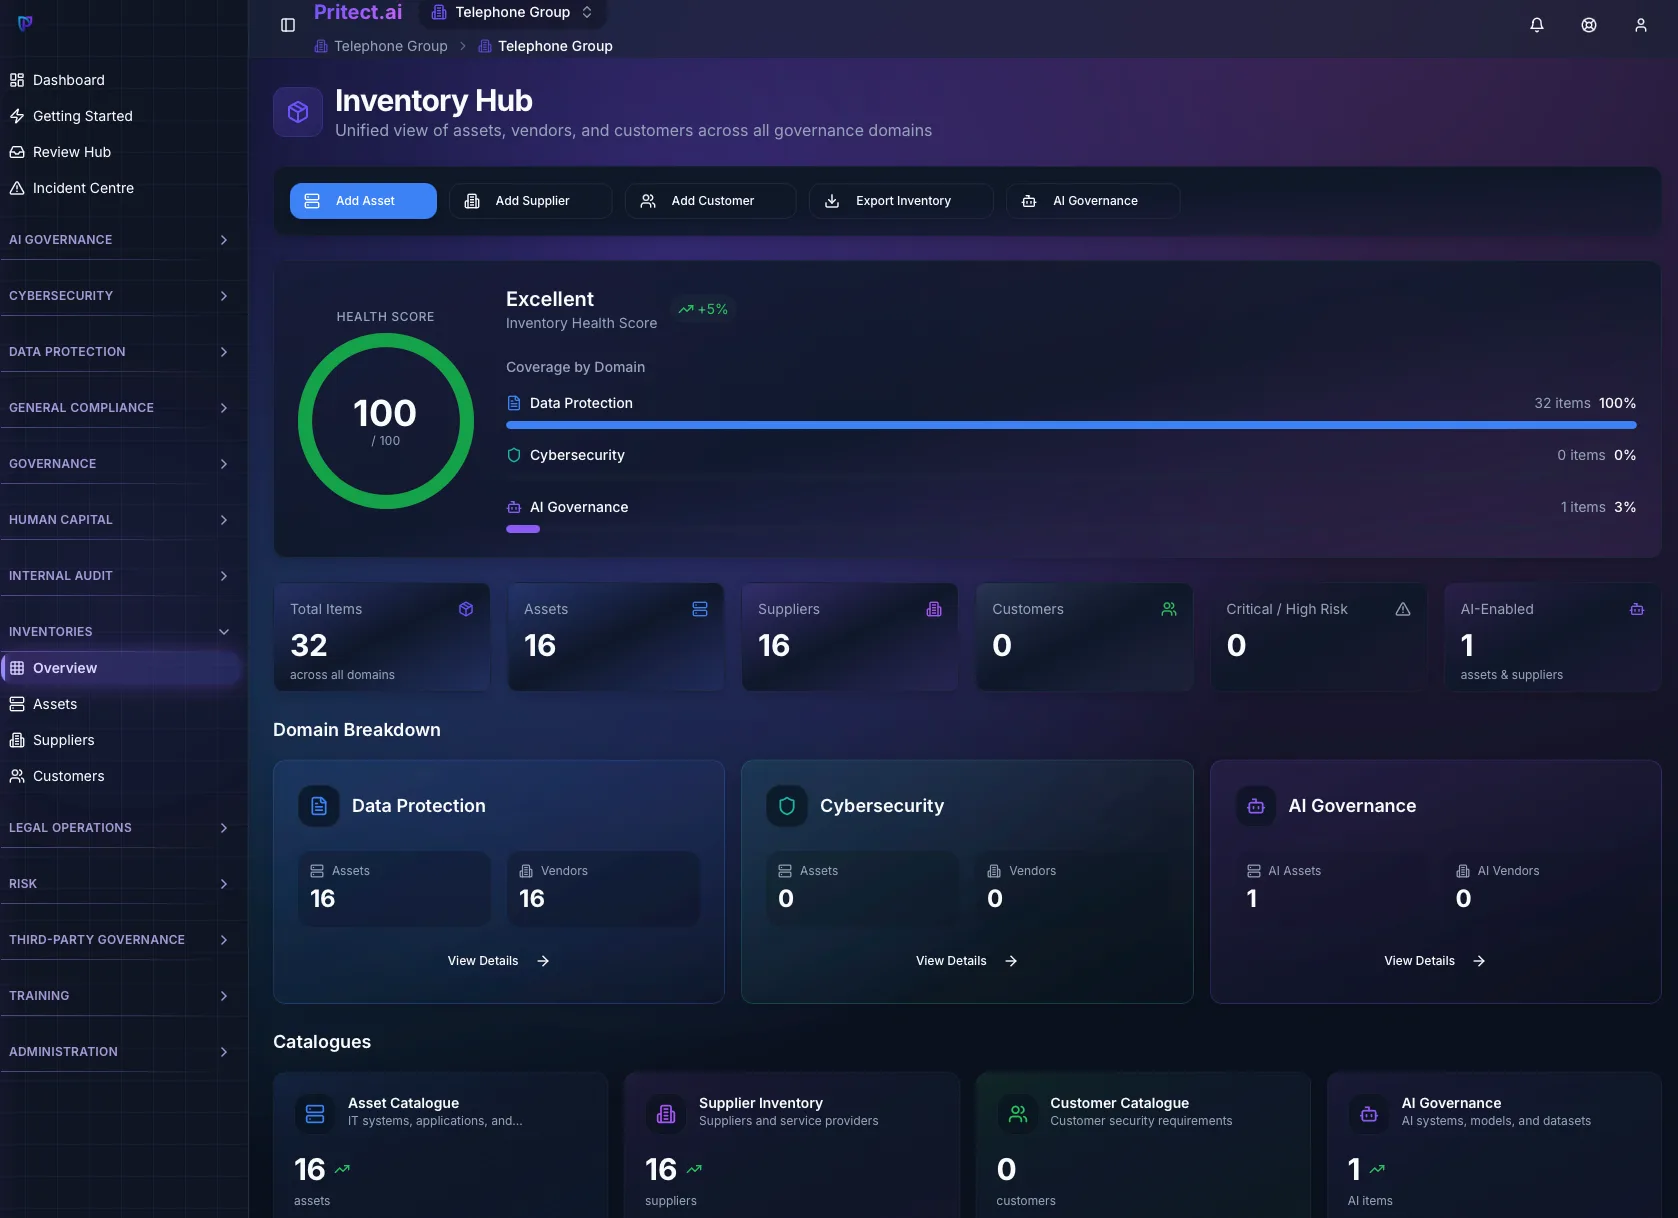
Critical Alerts
High-risk item tracking
AI Integration
AI assets & suppliers
Trend Analysis
Monitor progress over time
One Inventory, Four Perspectives
When you add an asset or supplier to your inventory, it automatically becomes available across all governance domains. No re-entry, no sync issues, no conflicting records, just seamless compliance coverage.
Data Protection
Assets become data sources in your RoPA. Suppliers become processors requiring DPAs. Every processing activity traces back to your inventory.
Cybersecurity
Assets form your attack surface for risk assessment. Suppliers become ICT providers under NIS2. Critical assets drive your BIA and recovery planning.
AI Governance
AI systems inherit asset metadata. AI suppliers require enhanced due diligence. Risk classifications flow from inventory to conformity assessments.
Enterprise Risk
Every inventory item carries risk context. High-risk suppliers aggregate into your risk register. Critical assets drive operational risk assessments.
The Inventory Lifecycle
Four integrated phases to build, organise, discover, and monitor your governance inventories
Catalogue
Build your registers
Create comprehensive registers of IT assets, suppliers, and customers with structured data collection and wizard-based entry.
- Asset Register
- Supplier Inventory
- Customer Catalogue
- AI Inventory
- Wizard-Based Entry
Classify
Organise by domain
Allocate items to governance domains and apply domain-specific attributes and classifications for precise compliance tracking.
- Multi-Domain Allocation
- Criticality Tiers
- Risk Ratings
- Data Classification
Discover
Find and filter
Powerful search and filtering across all inventories with domain-specific views and export capabilities.
- Global Search
- Domain Filters
- AI Assets Toggle
- Export Capabilities
Monitor
Track health and gaps
Monitor inventory health scores, identify gaps, and track compliance across all governance domains.
- Health Scoring
- Domain Coverage
- Critical Item Alerts
- Trend Analysis
Three Core Catalogues
Every organisation manages assets, works with suppliers, and serves customers. Our unified catalogues ensure these relationships are tracked consistently across every compliance requirement.
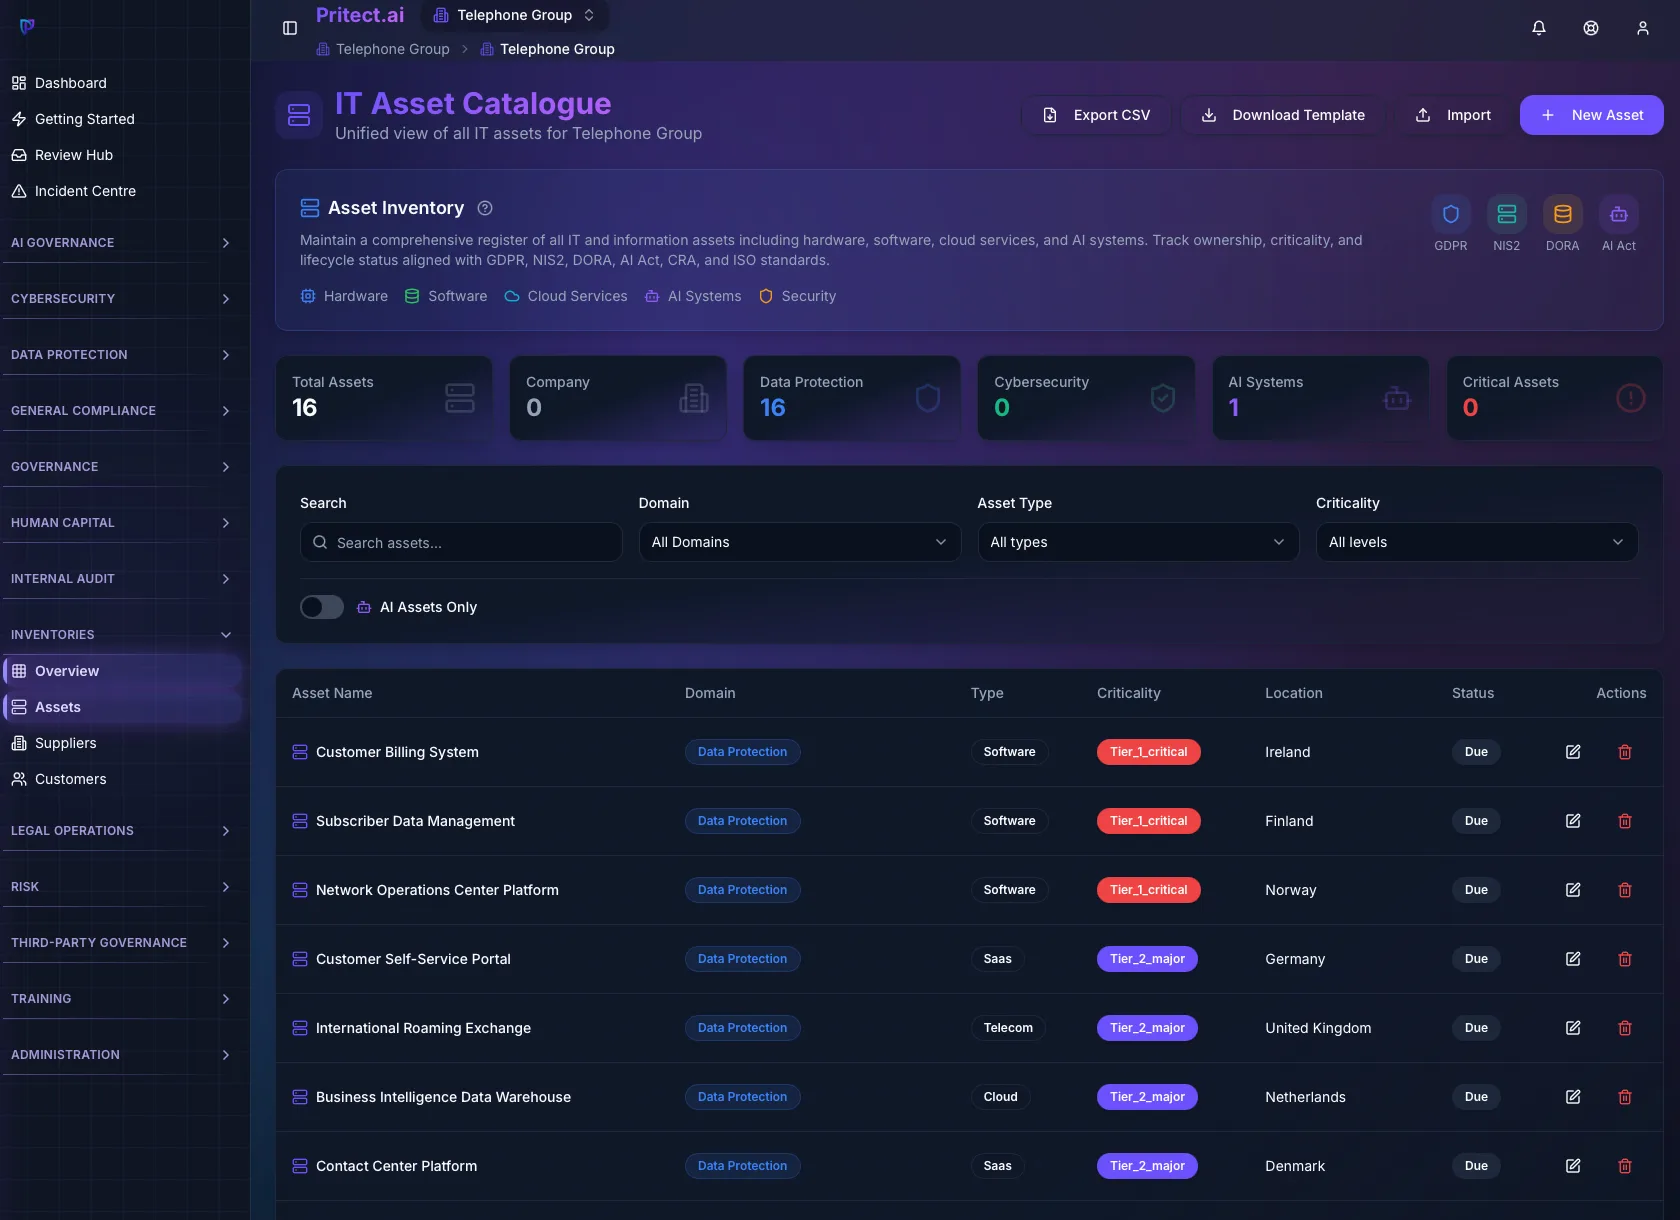
IT Asset Catalogue
Complete Asset Visibility
Your IT assets are the infrastructure that processes data, runs AI systems, and requires security controls. Track hardware, software, cloud services, and AI systems with criticality tiering that drives prioritisation across all governance domains.
Supplier Inventory
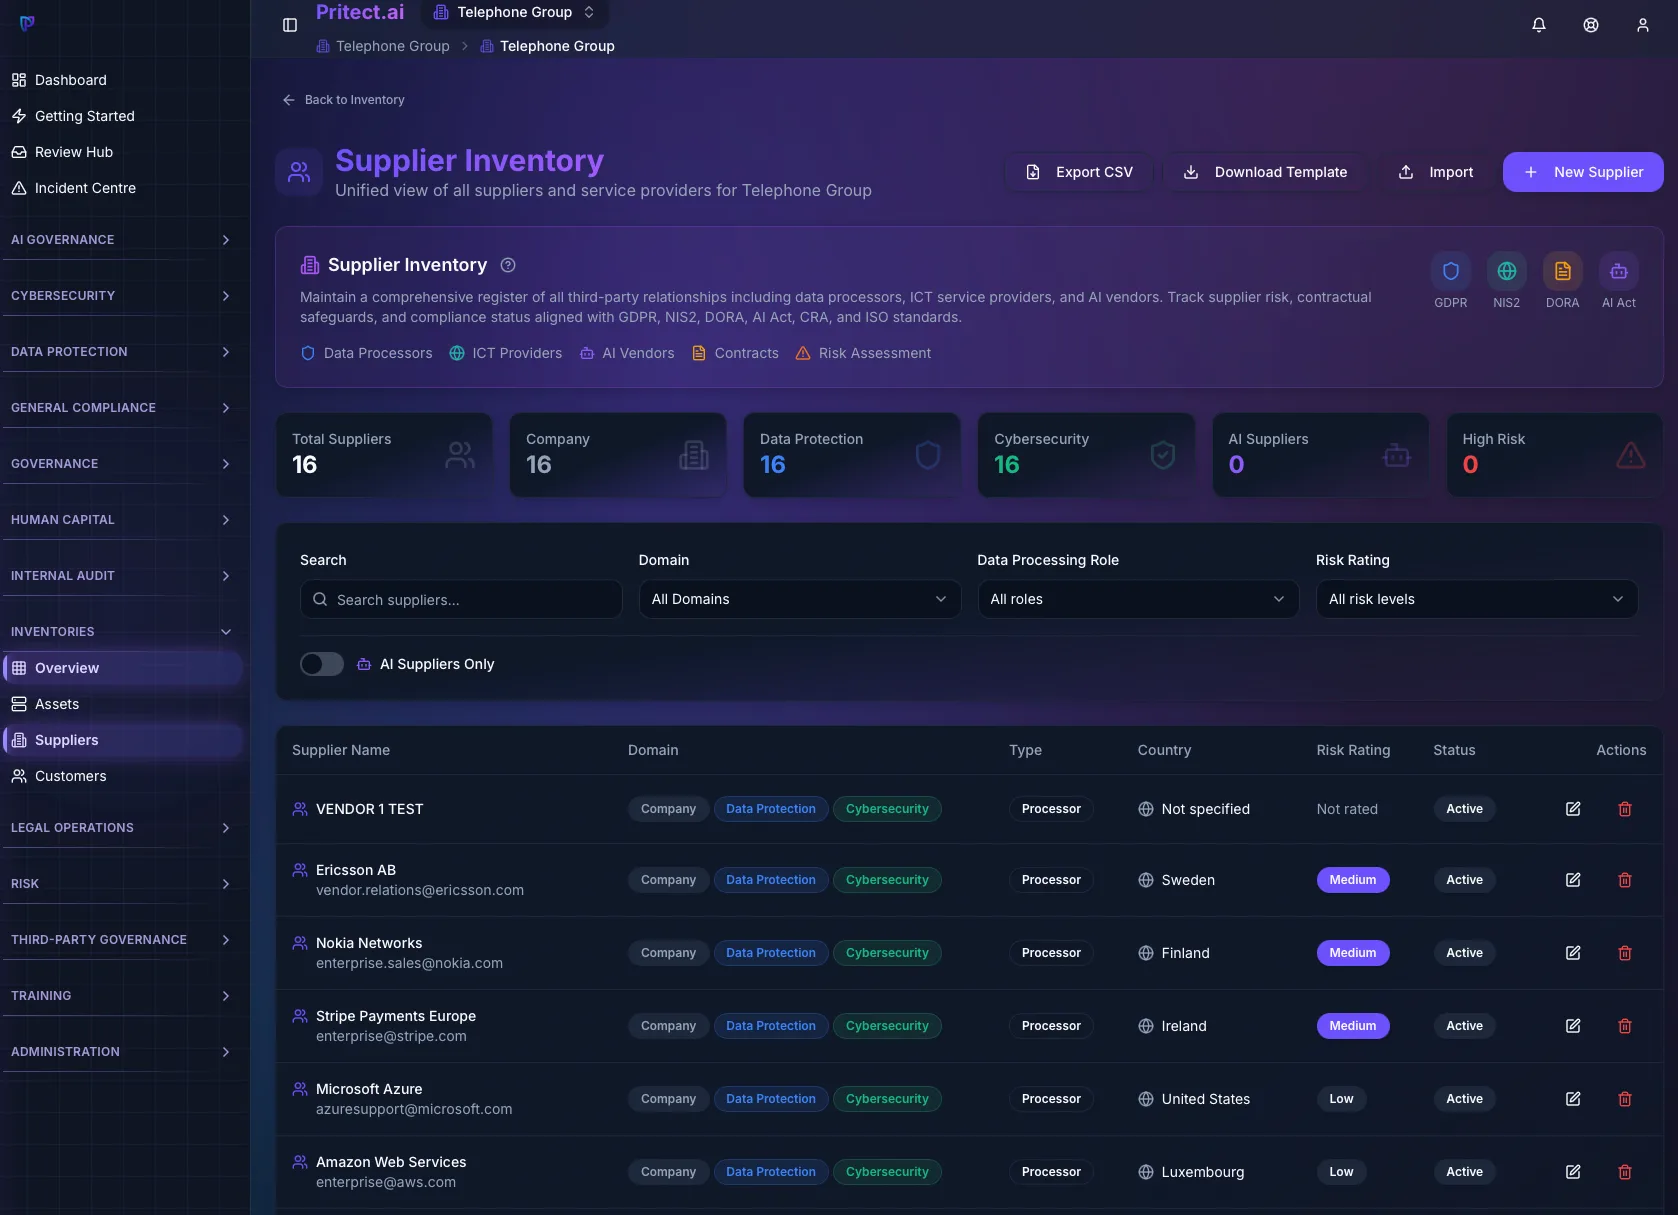
Third-Party Risk Visibility
Suppliers wear multiple hats in your compliance landscape: data processors for GDPR, ICT providers for NIS2, AI suppliers for the AI Act. Our unified supplier inventory captures all these relationships in one place, eliminating the chaos of scattered supplier lists.
Customer Catalogue
Customer Security Requirements
Your customers have security requirements too. Track contractual obligations, audit requests, and criticality assessments. When a strategic customer asks about your cybersecurity posture or AI governance, you'll have the answers ready.
Customer-Centric Compliance
Multi-Domain Allocation
One Item, Multiple Domains
A CRM system might be a data source for GDPR, a critical asset for NIS2, and an AI-enabled system under the AI Act. With multi-domain allocation, you capture all perspectives without creating duplicate records.
Result: One inventory record drives compliance tracking across all four domains: no duplication, no sync issues, complete traceability.
Enterprise-Ready
Built for organisations managing complex inventory requirements at scale
Multi-Entity Support
Manage inventories across corporate groups with hierarchical visibility and consolidated reporting.
Cross-Domain Inventory
Single source of truth across Data Protection, Cybersecurity, and AI Governance domains.
Import/Export
Excel template downloads, CSV exports, and bulk import with row-level validation and error feedback.
Regulatory Alignment
Built-in support for GDPR Articles 28, 30, 44-49, NIS2, DORA, and EU AI Act requirements.
Ready to Build Your Foundation?
Join organisations building a single source of truth for assets, suppliers and customers, the foundation that powers every governance domain.