Cybersecurity
Operating Environment
A structured lifecycle approach to cybersecurity governance, from discovery to response, built for organisations navigating NIS2, ISO/IEC 27001, and modern security frameworks.
A guided path to an audit-ready programme
Most security programmes stall not because nobody knows what to do, but because nobody knows what to do next. The Companion walks the programme with you, one stage at a time, and picks up where you left off.
- It reads what you already have before it asks you anything
- Every proposal cites the record it came from
- Nothing is written until you approve it
- Resumable, so the work survives the week it was started in
The through-line
The Cybersecurity Lifecycle
A structured approach to cybersecurity governance, from discovering your environment to responding to incidents.
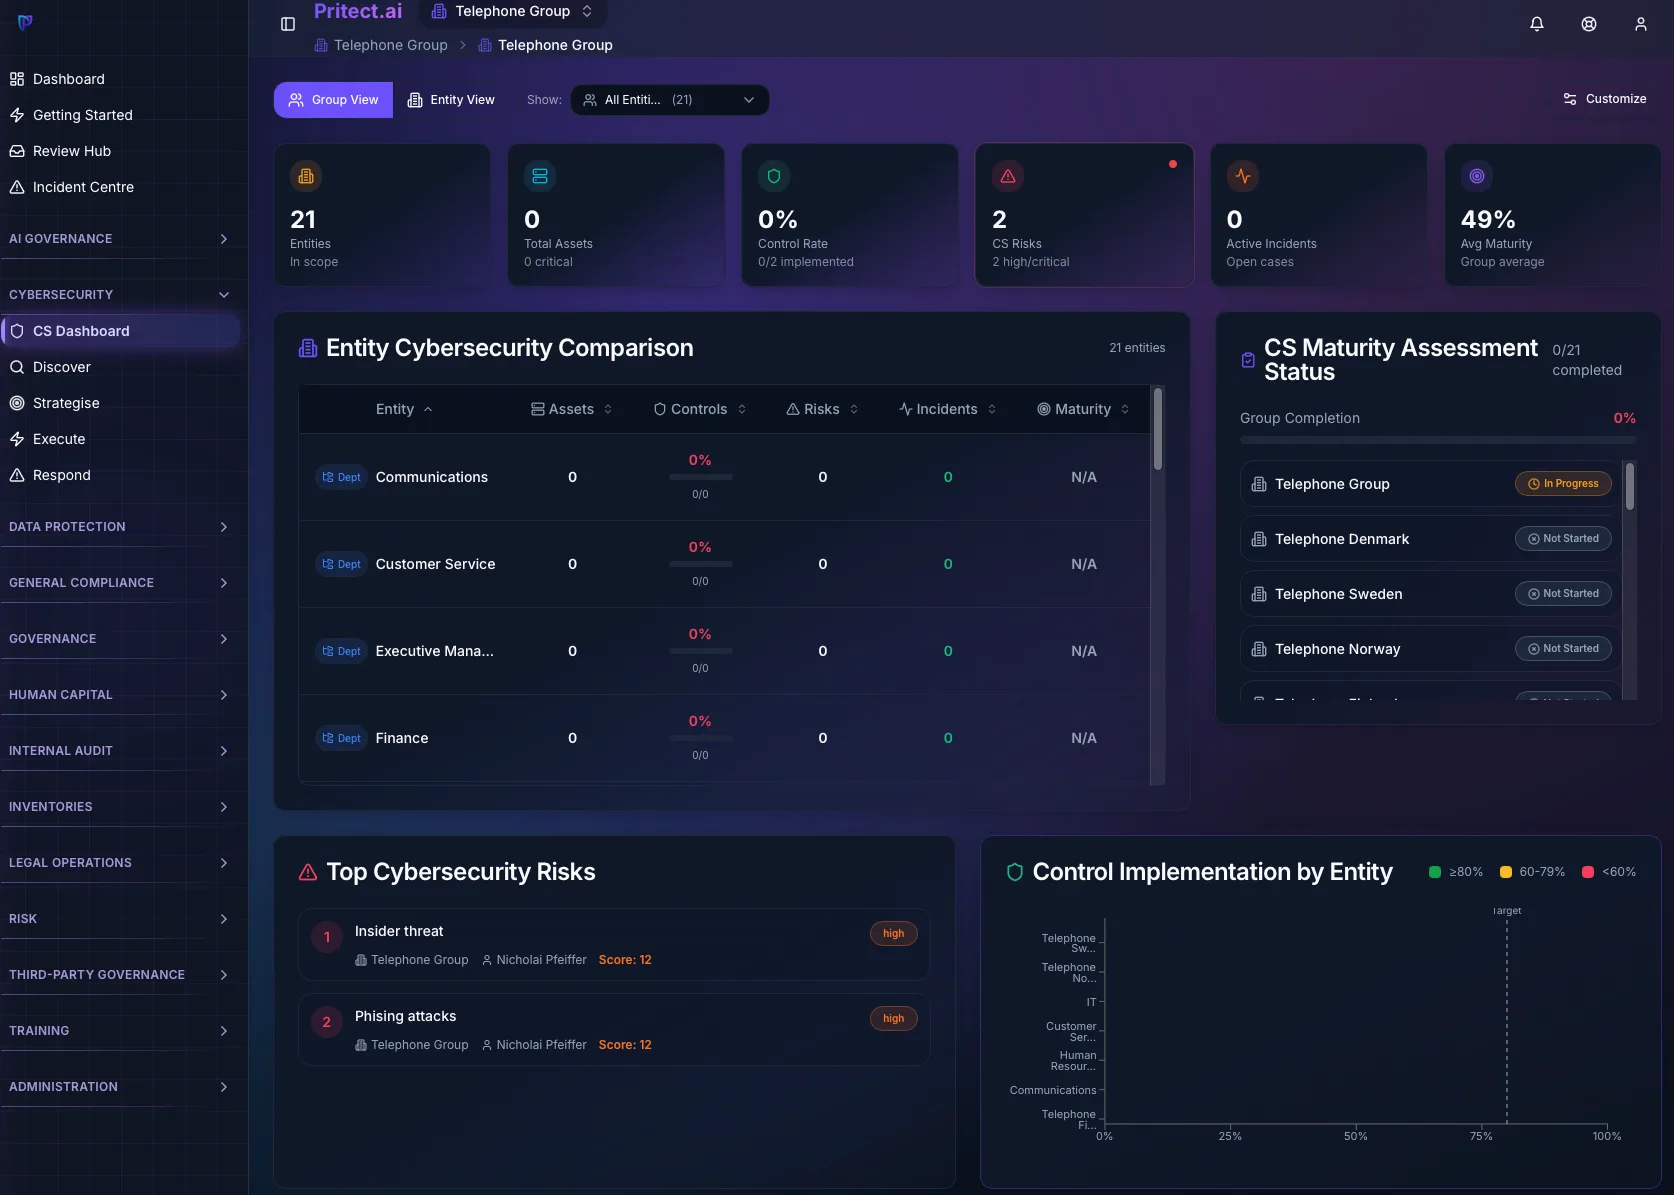
Discover
Know your environment
Build complete visibility into assets, threats, vulnerabilities, and business context across your organisation.
- Asset, service and supplier inventory
- Threat assessment, mapped to MITRE ATT&CK
- Vulnerability intelligence against public CVE data
- Business impact analysis, with RTO and RPO
- Security risk assessment on NIST SP 800-30
- Maturity assessment against the PCF
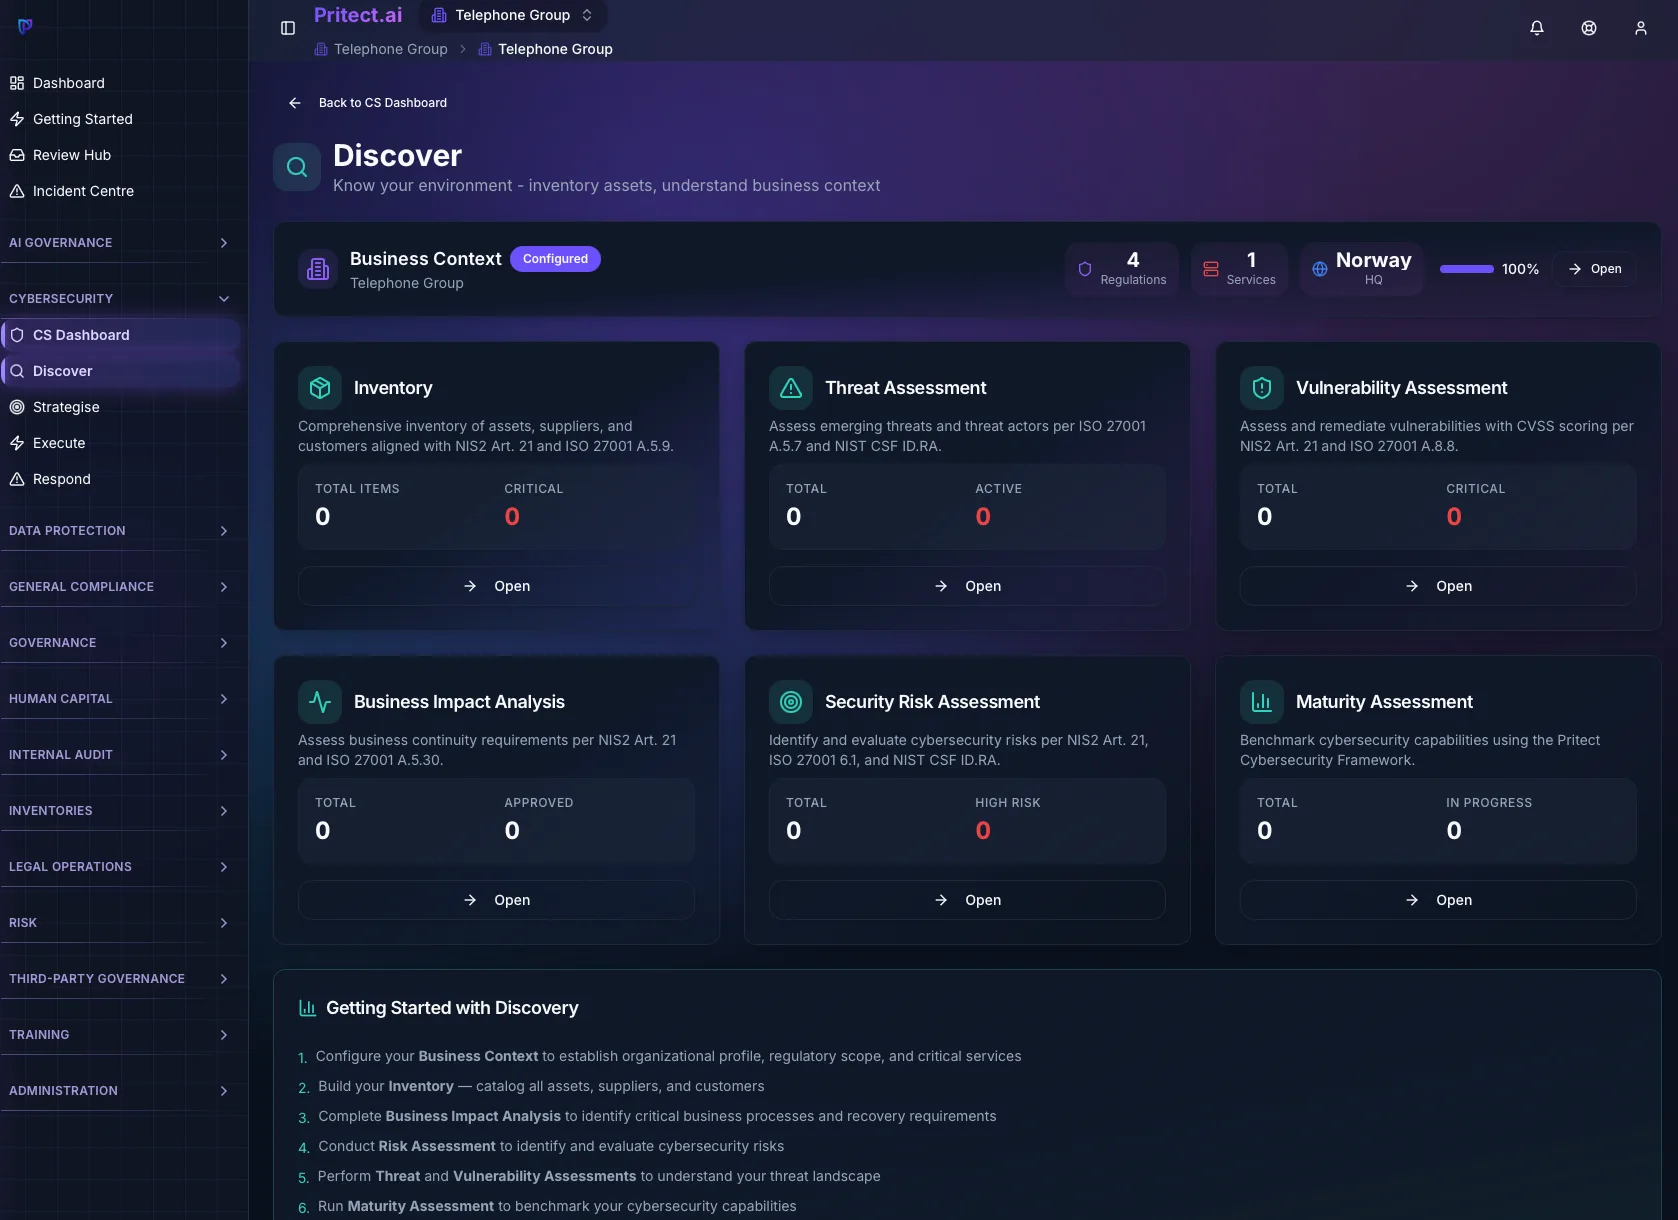
Strategise
Plan your defence
Define risk appetite, select security controls, and build your security roadmap.
- Risk tolerance and target maturity
- Security controls on the PCF
- Policies, standards and work instructions
- Exceptions, with an approval trail
- Risk register and mitigations
- Gap analysis against your target
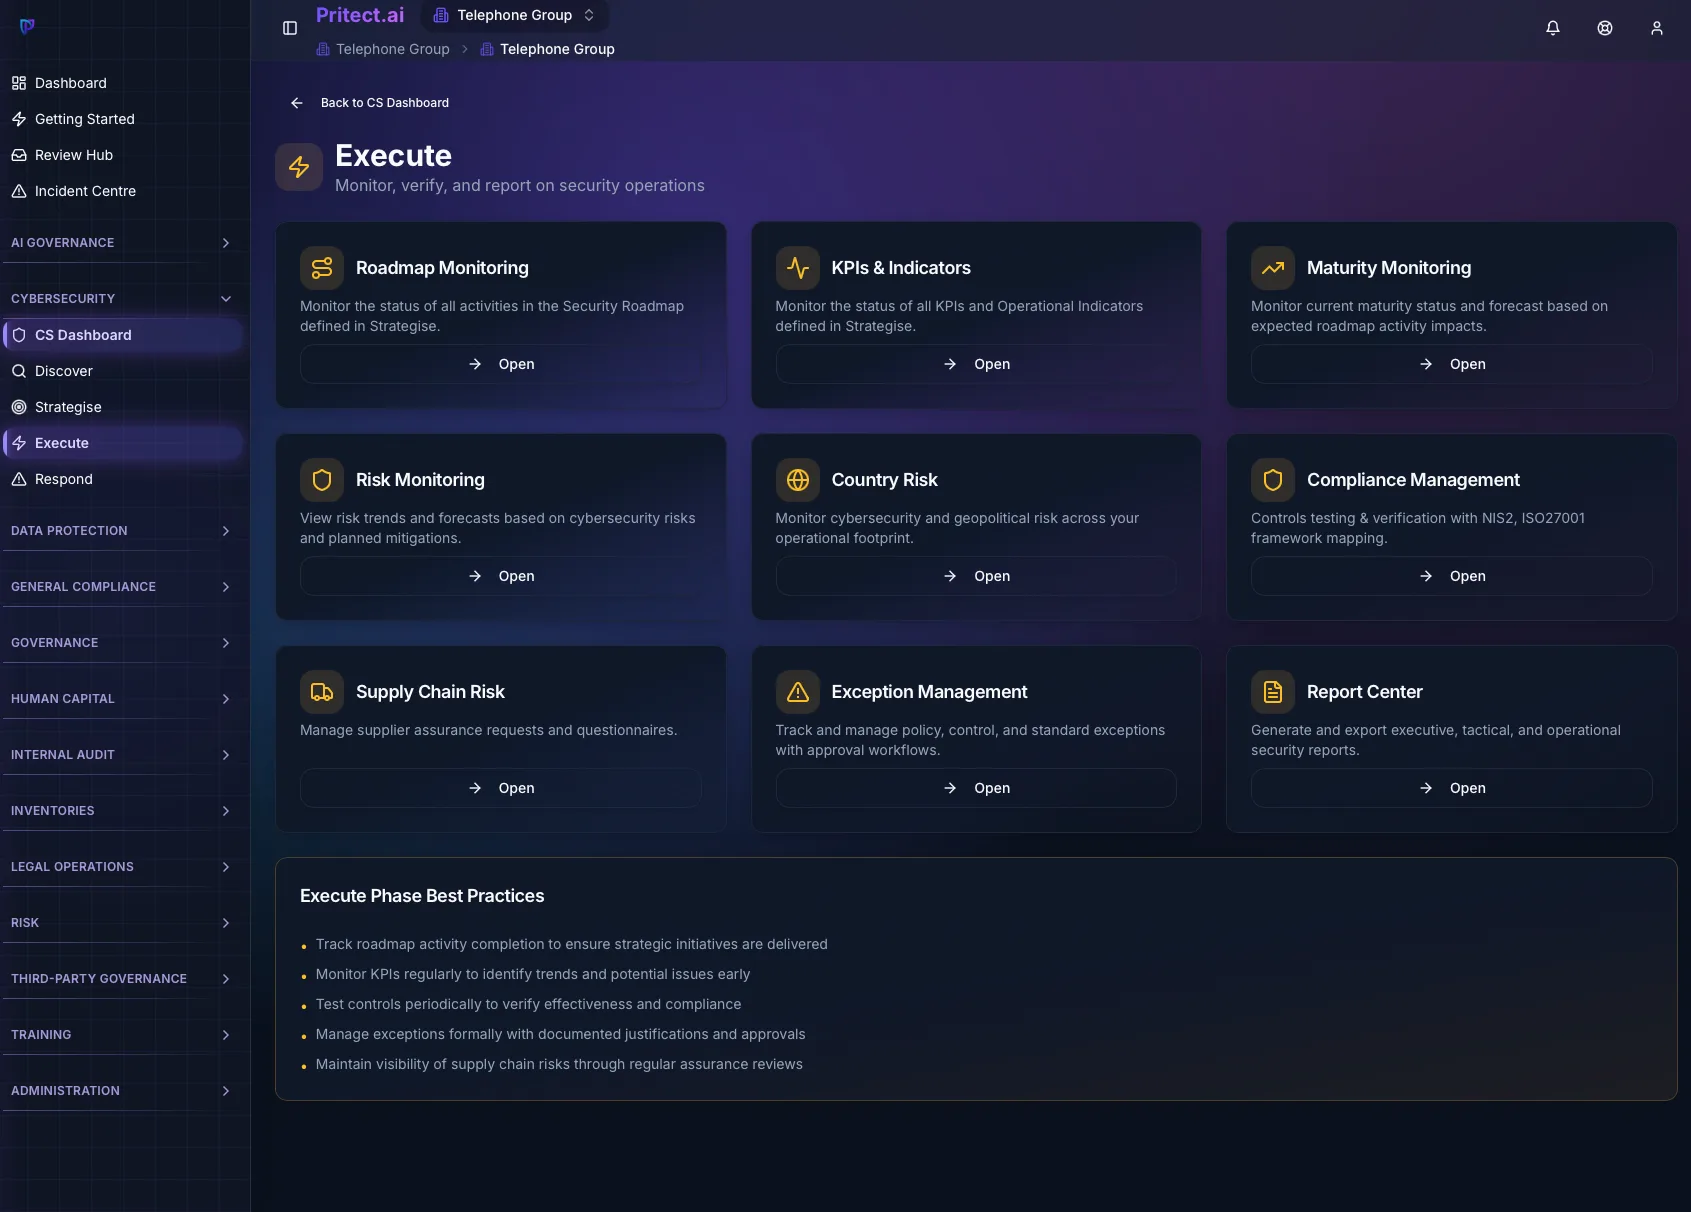
Execute
Monitor and verify
Track roadmap progress, monitor KPIs, and verify control implementation.
- Continuous control assurance, with drift detection
- Evidence locker, with freshness tracking
- Threat intelligence, correlated to your estate
- Security KPIs and regulatory coverage
- Supply chain risk
- Country risk intelligence
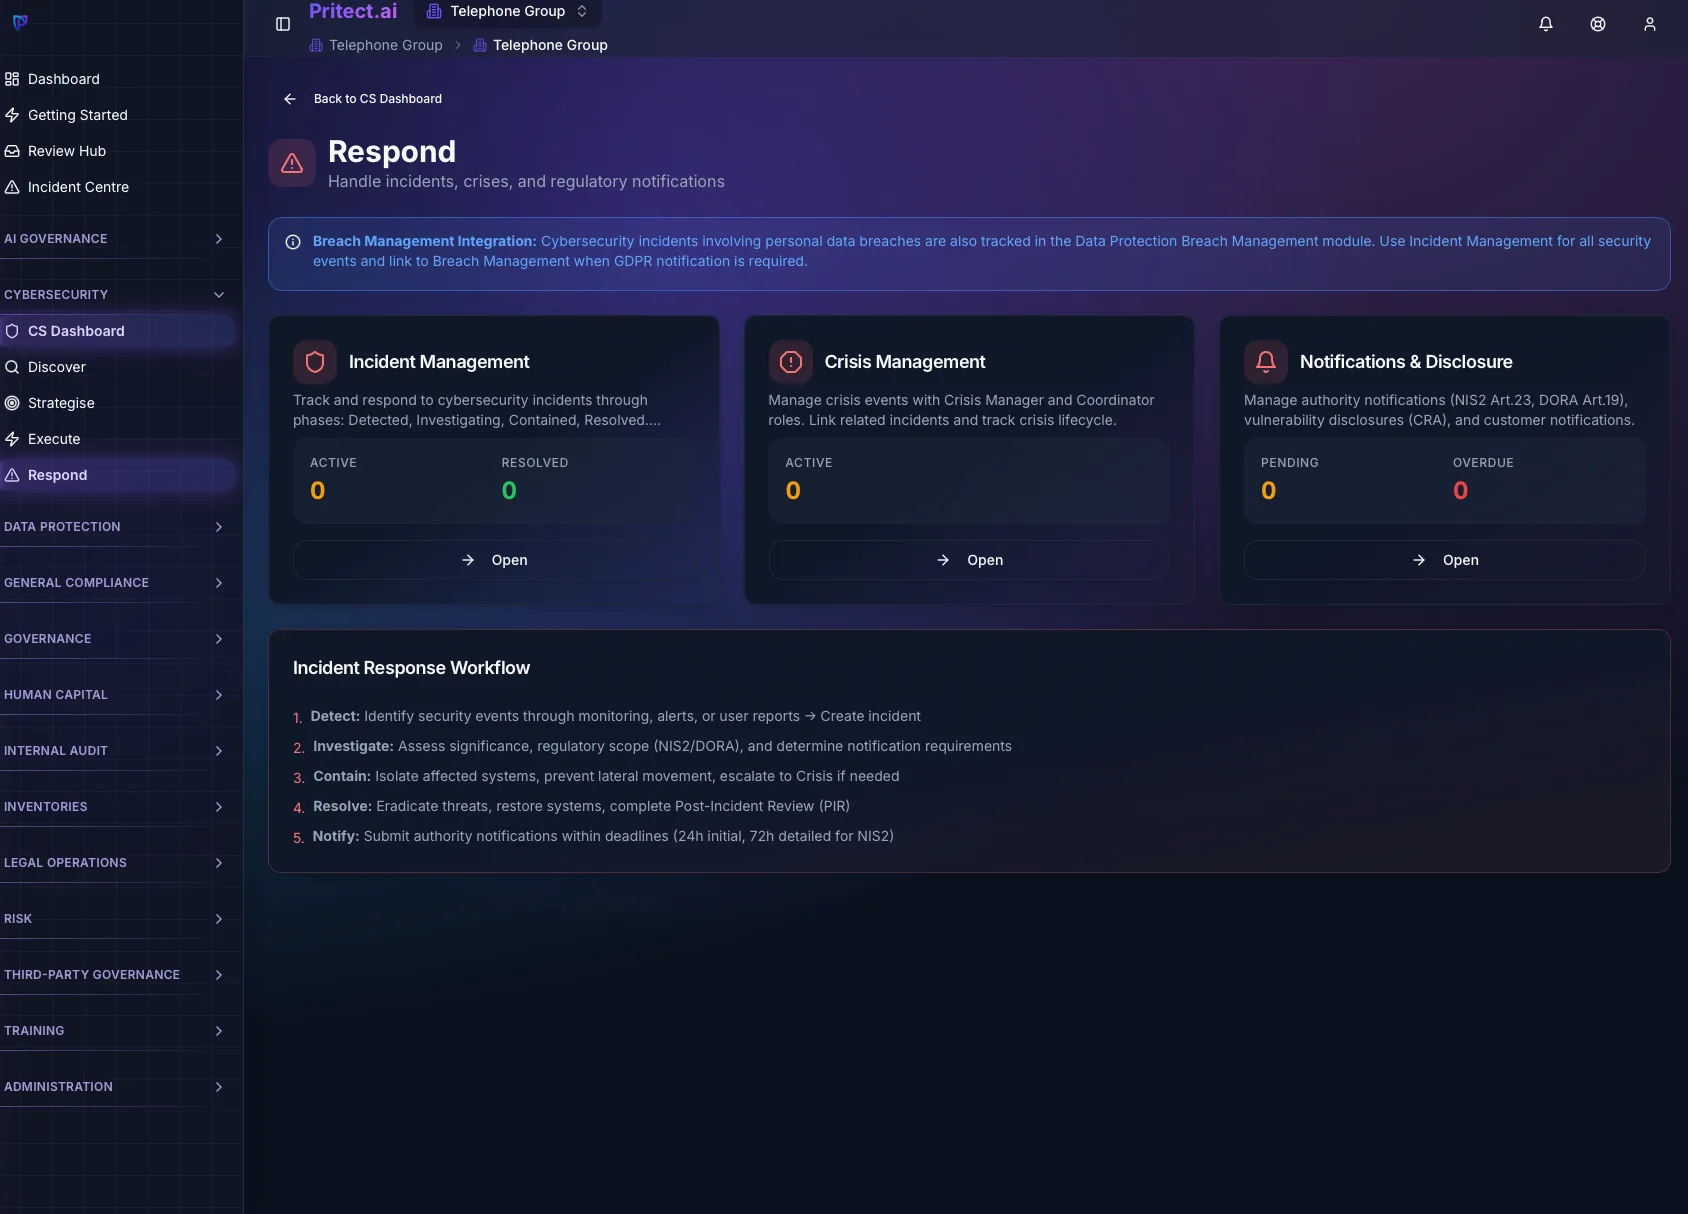
Respond
Handle incidents
Manage security incidents and crises with structured workflows and regulatory notifications.
- Incident management, on the platform Incident Centre
- Business continuity, tied to your BIA
- Disaster recovery, tested against real RTO and RPO
- Crisis command, with situation reports and decisions
- Authority notifications under NIS2, DORA and the CRA
PCF 1.0.0 Security Control Framework
330+ controls across 16 security domains, mapped to NIS2 and ISO/IEC 27001 requirements.
70
High-level Controls
202
Baseline Controls
330
Comprehensive Controls
16 Security Domains
6-Level Maturity Assessment
Assess your cybersecurity maturity across all domains using our 0-5 scale, set targets, and track progress over time.
- Entity-by-entity maturity comparison
- Gap analysis against target levels
- Historical trend tracking
- Benchmark against industry standards
- Executive-ready reporting
Maturity Levels
Incident Response Workflow
Structured five-step incident management with built-in NIS2 and DORA notification timelines.
Detect
Identify potential security incidents
Investigate
Analyse and assess the incident
Contain
Limit the impact and spread
Resolve
Remediate and recover
Notify
Report to authorities as required
Regulatory Notification Timelines
Initial notification to competent authority (NIS2 early warning)
Detailed incident notification with impact assessment (NIS2)
DORA initial notification, from classification and awareness, with the 72-hour intermediate report tracked automatically
Enterprise-Ready Capabilities
Built for complex organisations with multi-entity structures, regulatory requirements, and global operations.
Multi-Entity Support
Manage cybersecurity across complex corporate structures with cascading policies and entity-specific maturity tracking.
NIS2 & ISO/IEC 27001 Alignment
Built-in mapping to NIS2 Directive requirements and ISO/IEC 27001:2022 controls for regulatory compliance.
Supply Chain Risk
Assess and monitor security risks across your supply chain with structured due diligence workflows.
Country Risk Intelligence
Evaluate geopolitical and regulatory risks by country to inform security decisions and supplier selection.
Annual Security Wheel
Radial planning chart to visualise and schedule security activities across the entire year.
Evidence Locker
Centralised evidence management with versioning, review workflows, freshness tracking, and audit-ready exports.
Continuous Control Assurance
Delegate every control to the people who own it, test manually or against the systems you already run, and catch drift before an auditor does. Connects to GitHub and Microsoft 365.
Statement of Applicability
Produce an ISO 27001 Statement of Applicability, and registers for your regulations, standards and customer security requirements, from the same control spine.
Policy Management & AI Generation
Create, review, and approve security policies with AI-assisted drafting, version history, and approval workflows.
Ready to strengthen your cyber resilience?
Get started with the Cybersecurity Operating Environment or book a walkthrough with our team.
From the resource library
Related guides and analysis
- Capability deep-dive
Maturity assessments and gap analysis: how to actually raise your security and data protection posture
A practical guide to using maturity assessments, target setting, and gap analysis to move data protection and cybersecurity from ad hoc to managed, with the improvement loop that makes it stick.
9 min read - Guide
NIS2 compliance: what is actually required
A clear breakdown of NIS2 obligations for in-scope organisations, the management accountability it introduces, the reporting clock, and how to evidence security maturity over time.
7 min read - Perspective
AI in cybersecurity: the double-edged sword
AI strengthens defence and sharpens attacks at the same time. A practical look at the new threat surface, why AI systems themselves need securing, and how to keep it governed.
6 min read